Permissions and Roles
QFieldCloud provides fine-grained access control over projects and organizations using Project Collaborator roles and Organization Member roles.
Access permissions follow a strict hierarchy: a higher role automatically inherits all capabilities of lower roles.
Suggerimento
"Core Concepts Overview"
If you are new to QFieldCloud management, ensure you are familiar with these core concepts:
- Projects: The central repositories storing QGIS project files, layer datasets, styles, and field edits.
- Organizations: Shared accounts that own storage quotas, manage member subscriptions, and centralize project managements.
- Members: User accounts added to an organization with defined organization-level administrative roles.
- Collaborators: Individual user accounts granted specific access permissions to a single project.
Project Collaborator Roles
Project roles determine what an individual user can do within a specific project.
| Role | Summary |
|---|---|
| Owner / Admin | Full control over the project, including renaming, deleting, managing secrets, and modifying restricted project files (.qgz/.qgs). |
| Manager | Can manage project collaborators and dataset files. (Organization projects only) |
| Editor | Can create, update, and delete features and their attributes in the field. (Organization projects only) |
| Reporter | Can download the project and collect new features in the field, but cannot edit or delete existing features. |
| Reader | Read-only access to view and download the project. Cannot upload edits or changes. |
Note
To assign more than one collaborator on private projects, the project must belong to an organization plan and collaborators must all be members of that organization. Alternatively, you can make a project "public" allowing all QFieldCloud users to access your project.
Project Capabilities
The following table details what each project role can do:
| Capability \ Role | Reader | Reporter | Editor | Manager | Admin / Owner |
|---|---|---|---|---|---|
| View and download project files | ✅ | ✅ | ✅ | ✅ | ✅ |
| Collect NEW features in the field | ❌ | ✅ | ✅ | ✅ | ✅ |
| UPDATE or DELETE existing features | ❌ | ❌ | ✅ | ✅ | ✅ |
| Upload datasets (e.g., GeoPackages) | ❌ | ❌ | ✅ | ✅ | ✅ |
| Manage project collaborators | ❌ | ❌ | ❌ | ✅ | ✅ |
| Manage project secrets & service credentials | ❌ | ❌ | ❌ | ❌ | ✅ |
Upload restricted project files (.qgz, styles) |
❌ | ❌ | ❌ | ❌ | ✅ |
| Rename or delete the project | ❌ | ❌ | ❌ | ❌ | ✅ |
Organization Member Roles
Organizations consist of multiple members with different levels of administrative rights, ranging from basic membership to administrating the billing pages of the organization. Below is a table that outlines the different existing organization roles.
| Role | Summary |
|---|---|
| Owner | Primary administrative authority. Full access over organization billing, subscription plans, ownership transfers, member management, and all organization projects. |
| Admin | Administrative manager. Can manage organization members, structure teams, and manage all organization projects. |
| Creator | Project creation specialist. Can create new projects under the organization and manage projects they have created, without administrative access to organization billing or member lists. They are automatically set as administrators of the newly created projects. |
| Member | Standard organization user. Assigned to specific organization projects as a collaborator. Membership distinction primarily serves organizational visibility and billing seat allocations. |
Organization Capabilities Matrix
The following table details what each organization role can do:
| Capability \ Role | Member | Creator | Admin | Owner |
|---|---|---|---|---|
| View organization member directory & teams | ✅ | ✅ | ✅ | ✅ |
| Access assigned organization projects | ✅ | ✅ | ✅ | ✅ |
| Create new projects under the organization | ❌ | ✅ | ✅ | ✅ |
| Add, remove, or modify organization members | ❌ | ❌ | ✅ | ✅ |
| Manage organization teams & team roles | ❌ | ❌ | ✅ | ✅ |
| View billing, active users, and invoices | ❌ | ❌ | ❌ | ✅ |
| Modify plan subscriptions & payment details | ❌ | ❌ | ❌ | ✅ |
| Delete organization or transfer primary ownership | ❌ | ❌ | ❌ | ✅ |
Default Project Role for Organization Members
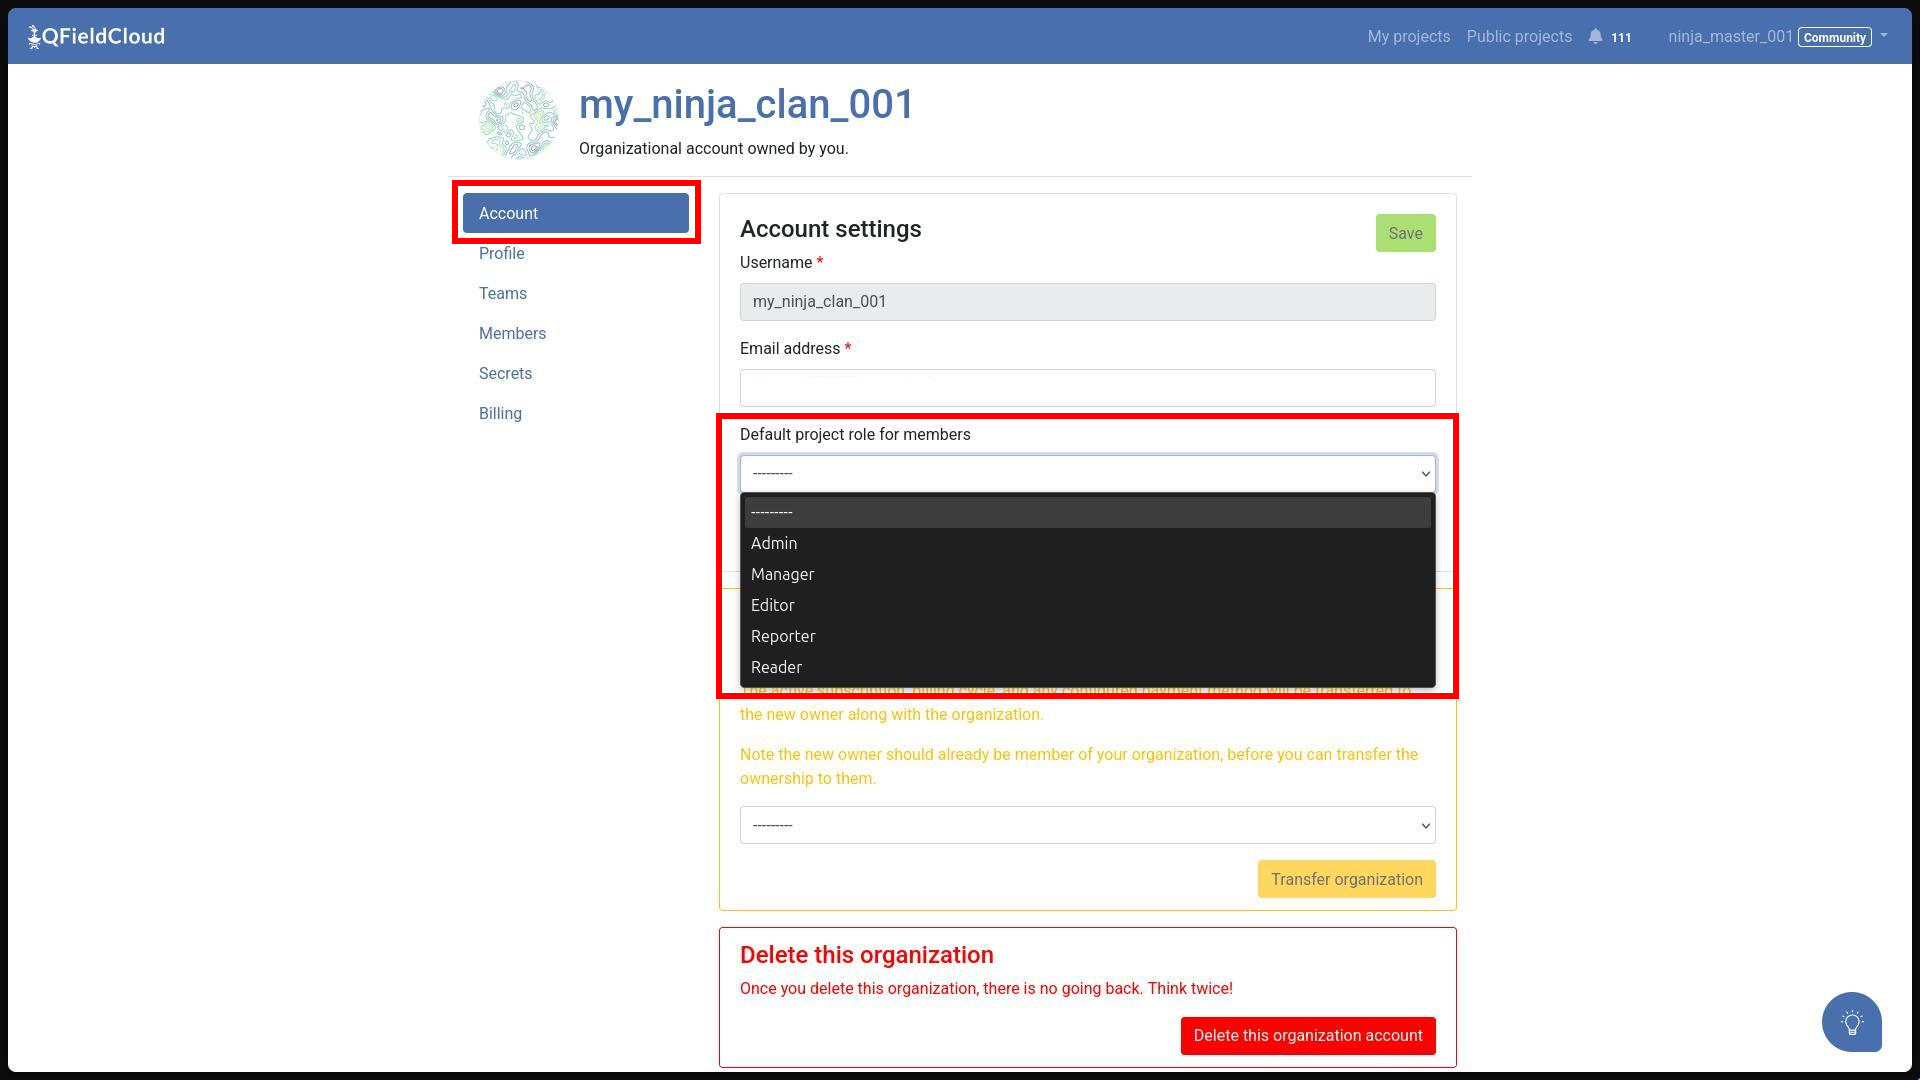
As an organization, you have the option to configure a Default Project Role for Members in the Organization settings.
When you add organization members to an organization project, QFieldCloud automatically assigns this default role without requiring manual changes to the collaborator role for each newly added collaborator.
Key Security Features
Restricted Project Files
When the Restrict project files setting is enabled on a project, standard Editors and Managers can continue updating datasets (such as GeoPackages), but they are blocked from modifying or replacing core project files (such as .qgz or .qgs project files and style templates).
Only Admins and Owners can modify restricted files.
Private vs. Public Projects
Each project can be configured as Private or Public when creating a project or inside the project settings:
Workflow
Project Manager
- Log into QFieldCloud and select your project.
- Navigate to Settings in the project menu.
- Check or uncheck Is public.
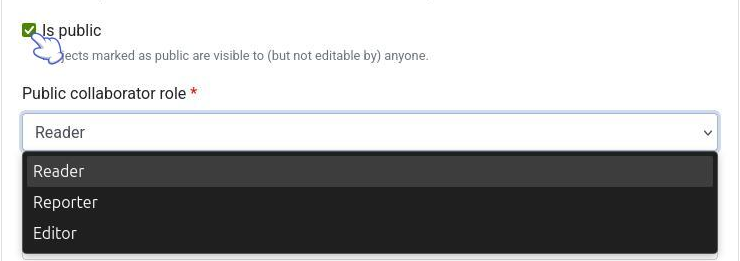
In QFieldCloud, the status icon next to the project name indicates project visibility: a lock icon (🔒) represents a Private project, while an unadorned project title represents a Public project.
- Private Projects: The project owner, organization owner, and organization admins are automatically assigned the Admin project role. Anyone else trying to access the project will be denied unless they are explicitly added as project collaborators.
Note
To assign collaborators on a Private project owned by an organization, all candidate collaborators must be members of that organization. In addition, the total number of collaborators cannot exceed the owner's subscription plan limits.
- Public Projects: The project owner, organization owner, and organization admins automatically receive the Admin project role. All other authenticated QFieldCloud users receive a default base permission defined by the Public Collaborator Role.
Public Collaborator Role
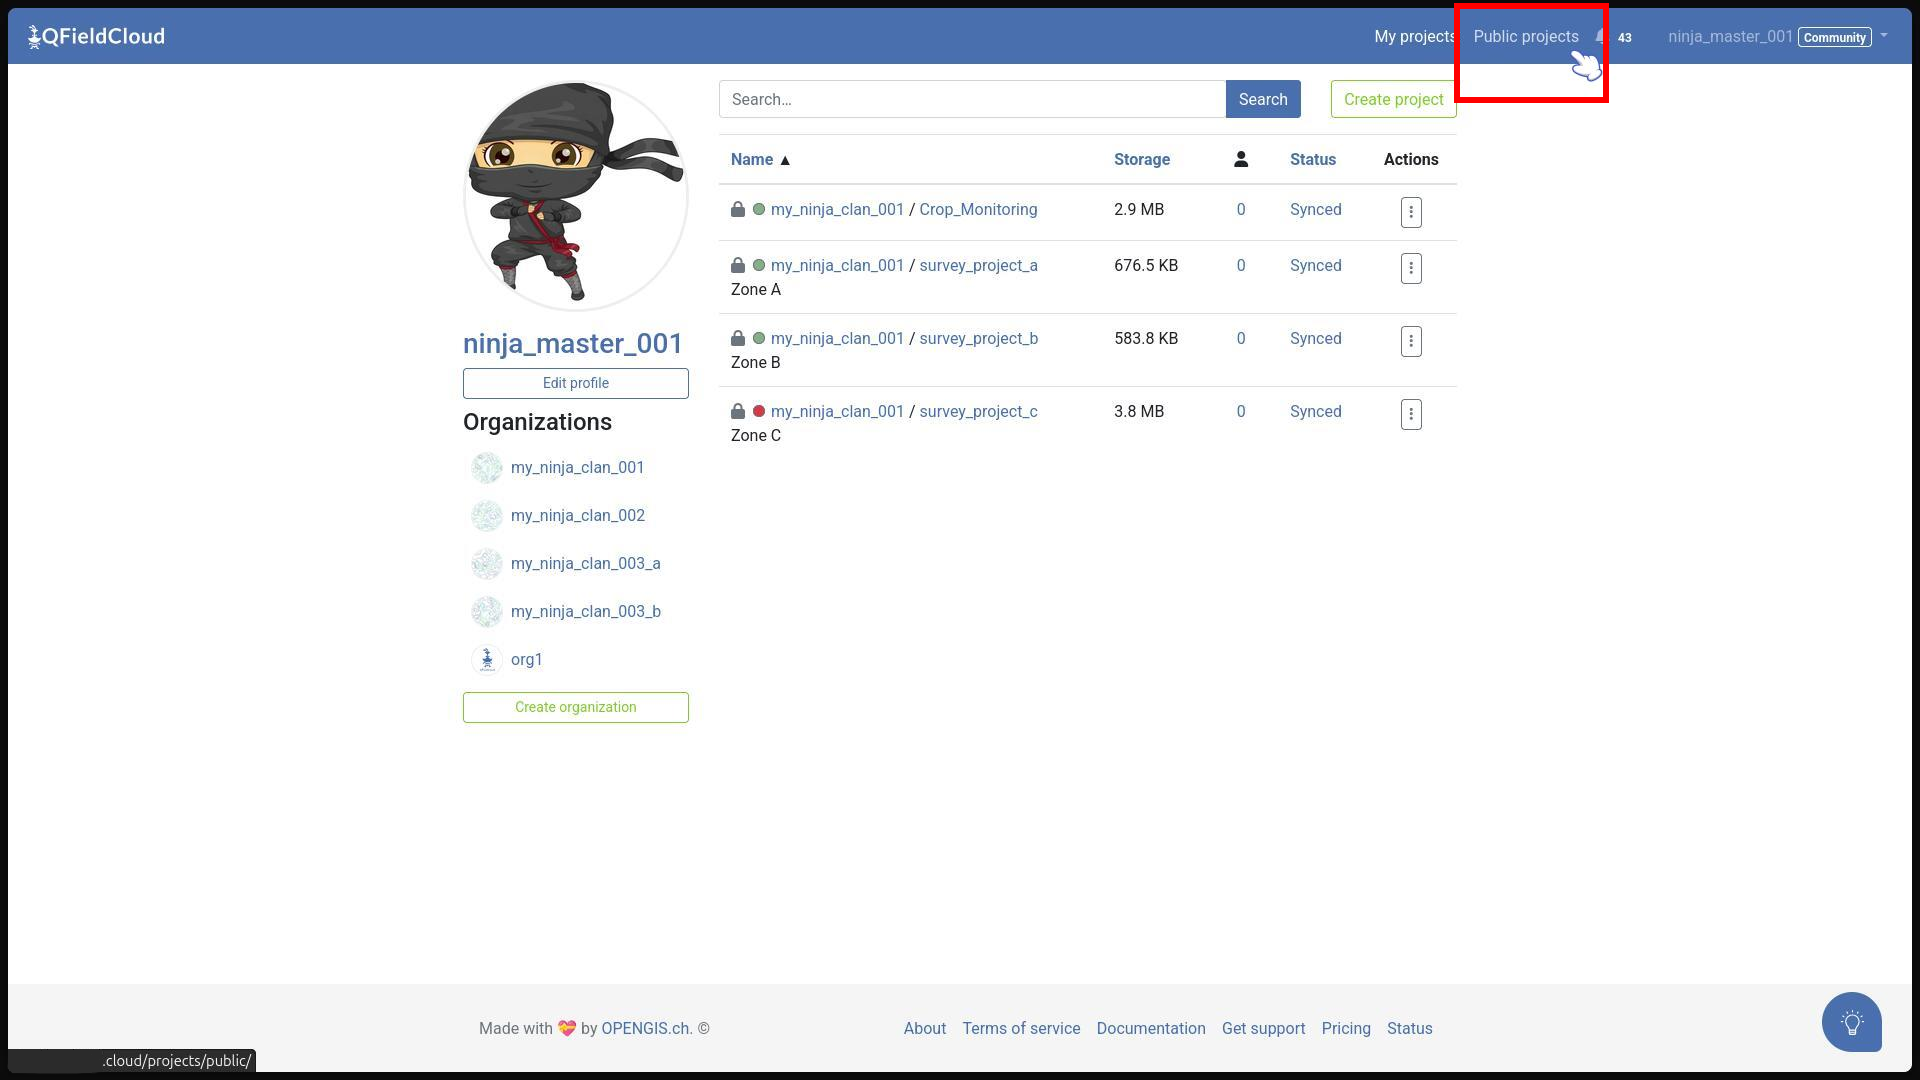
When you enable Public project while creating a project, or while configuring project settings, a Public collaborator role field will automatically show up below the checkbox.
This setting defines the default role granted to any QFieldCloud user who wishes to use that public project:
- Public Collaborator Role: You can choose between the roles Reader (read-only access), Reporter or Editor. Read here about which role is appropriate for your needs.
- Default Role: If you mark a project as public and do not define the Public Collaborator role, it will default to the Reader role.
- External Non-Member Collaborators: Users who aren't part of the organization can be added as collaborators on public projects without becoming organization members. Be aware that changing a public project to private interrupts the process if collaborators aren't part of the organization, and you will need to either remove them from the project or add them to the organization.
Converting Public Projects to Private
When switching a Public project to Private, QFieldCloud enforces validation checks before saving the change:
- Check for Non-Organization Members: If collaborators on an organization project are not members of the organization, you must remove them or add them as organization members before making the project private.
- Check for Subscription Plan Limits:: The total collaborators must not exceed the collaborator limit on the project owner's subscription. Remove additional collaborators before setting visibility to private.
Note
If a subscription downgrade occurs on an existing private project that exceeds the plan limit, the system keeps the project private but locks it until the user reduces collaborator counts to within plan limits or upgrades the plan.